Employee privacy, personnel records, biometric attendance, CCTV and workplace communications under Turkish law.
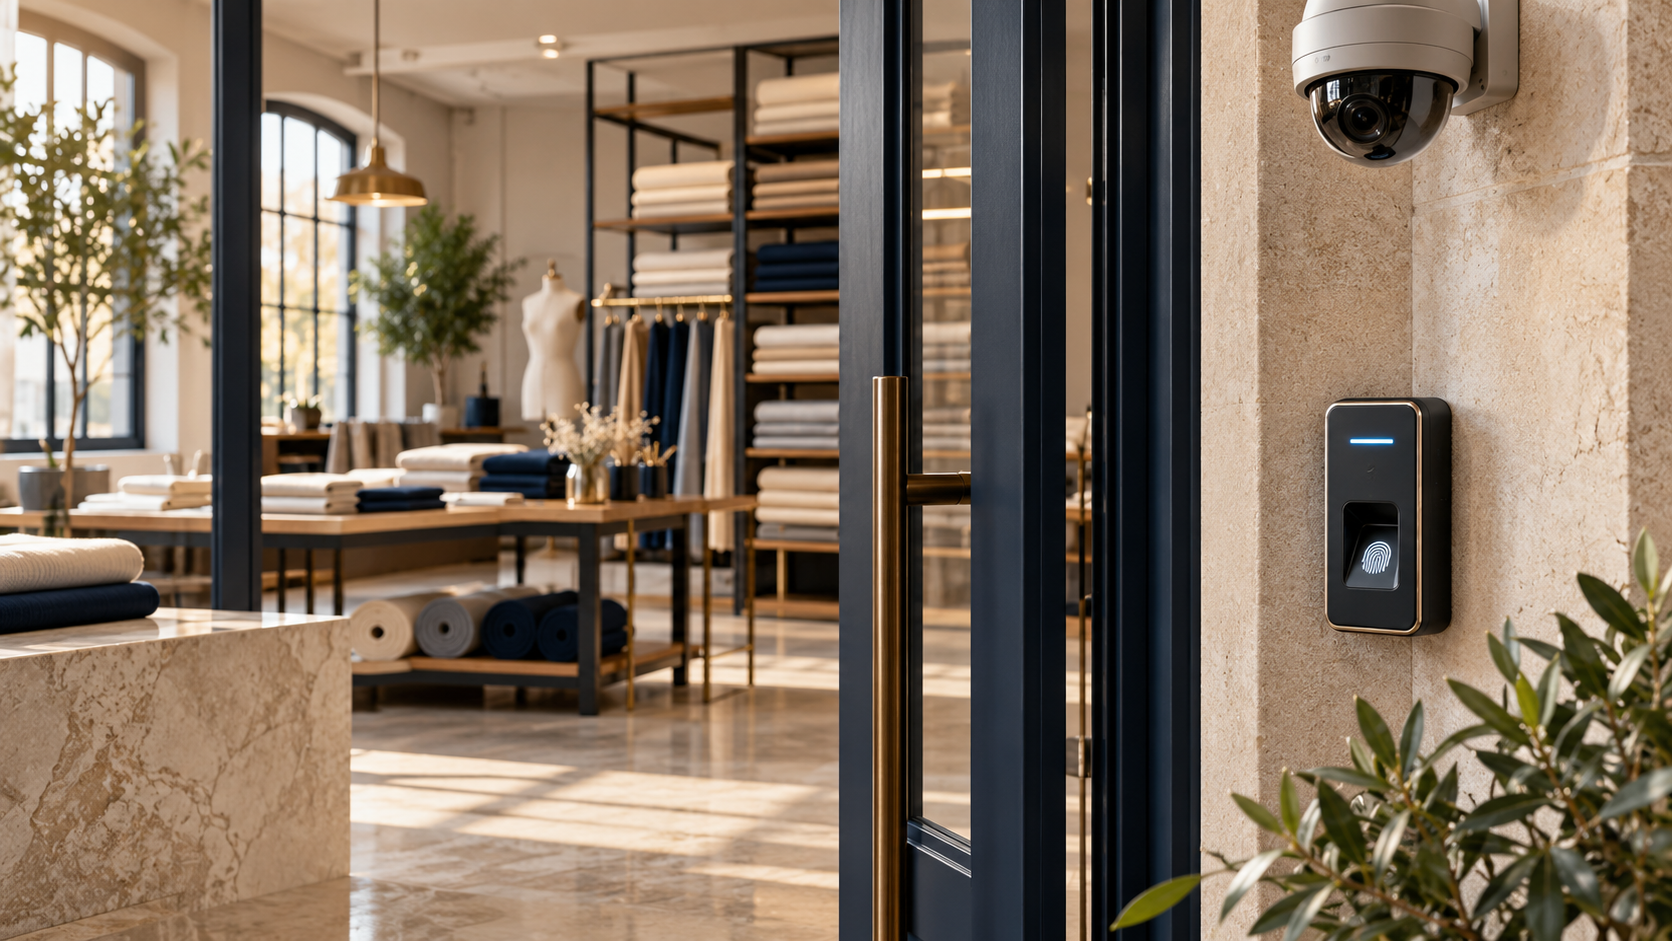
From recruitment to termination, textile businesses process substantial volumes of employee information. Personnel files, medical reports, attendance records and surveillance require separate legal assessments.
An employer’s management powers do not remove employees’ rights to privacy and protection of their personal data. Each processing activity needs a specific purpose, an applicable legal basis and proportionate safeguards.
1. Personnel records and retention
Employers hold identity, contact, bank, education, social security, payroll and attendance information to meet employment obligations. Depending on the activity, ordinary personal data may be processed where expressly required by law, necessary for a contract or necessary to fulfil a legal obligation. Consent is not required where another applicable legal basis exists. Health information and other special categories require a separate assessment under Article 6.
Provide an employee privacy notice when collecting the data and retain evidence that it was provided. A notice is not a request for consent.
Collect only information connected with the specified purpose. Do not add documents to personnel files merely because they might be useful someday.
Restrict access to authorised HR staff and managers according to their roles, and log access where appropriate.
Set retention periods by record type, considering employment, social security, tax and other applicable rules. There is no single retention period for every personnel document. Delete, destroy or anonymise data when the lawful grounds for retention cease.
Specify an appropriate retention period for unsuccessful candidates’ CVs; do not retain application data indefinitely.
2. Health and other special categories of data
Medical reports, pre-employment and periodic examination findings, disability information and trade union membership are subject to enhanced protection.
Following the 2024 amendment to Article 6, processing necessary to fulfil legal obligations concerning employment, occupational health and safety and the other areas listed in that article has its own legal basis. This does not authorise unrestricted access or collection beyond what is necessary.
3. Fingerprints and biometric attendance: Decision 2026/921
The Personal Data Protection Board’s principle decision of 29 April 2026, No. 2026/921, was published in Official Gazette No. 33268 on 2 June 2026. It concerns biometric processing for attendance tracking, including fingerprints, facial recognition, iris and retina data.
What the decision means
Biometric data are special category personal data. The imbalance in employment relationships raises serious questions about whether consent is freely given.
Where less intrusive attendance methods are available, such as a card, PIN, RFID/NFC badge or signed attendance sheet, collecting biometrics for this purpose fails the proportionality requirement even if consent is obtained.
Converting a biometric identifier into a mathematical code or template does not automatically take it outside biometric data protection rules.
The decision specifically addresses attendance. Other uses, including access to a critical security area, require their own legal assessment; being outside this decision’s scope is not automatic permission.
Textile businesses using fingerprint or facial attendance systems should review their practices, move to appropriate alternatives and deal lawfully with stored biometric templates. Update notices, internal inventories and VERBIS entries where relevant. Follow the Board’s text and subsequent announcements rather than assuming an unverified grace period.
4. CCTV and communications monitoring
Workplace CCTV
Security cameras may have an applicable Article 5 basis, such as a properly assessed legitimate interest or a specific legal obligation. They must still satisfy necessity, transparency and proportionality.
Identify a concrete security purpose. A security installation must not become general surveillance of private life or continuous employee performance monitoring.
Avoid cameras in toilets, changing rooms and other areas with a high expectation of privacy, including private rest areas. Assess viewing angles and the scope of recording.
Use visible signs and provide the required privacy information to employees and other affected persons.
Limit authorised access and keep recordings only for a justified period related to their purpose.
Audio recording is more intrusive. It requires a separate lawful basis and a convincing necessity assessment; video surveillance does not itself justify recording sound.
Corporate email, telephones and messaging
The Constitutional Court’s Fırat Gerçek judgment, application No. 2019/25604, dated 21 September 2022, concerned private messages between colleagues on a mobile phone. It should not be described as granting employers a general power to inspect corporate email. Its privacy and freedom of communication analysis underlines the importance of a legitimate purpose, transparency and proportionate interference.
Reviewing communications traffic and reading message content involve different levels of interference. Content inspection requires stronger, specific justification. Work-related use of a personal WhatsApp account does not give the employer unrestricted access to private messages.
Update: 30 October 2026
The Board’s principle decision of 16 September 2026, No. 2026/2035, announced on 8 October 2026, addresses monitoring corporate email and other communication channels used for work. Employers should give clear prior information, define legitimate purposes and use graduated, less intrusive methods. Content review requires a concrete suspicion or particular event; vague and continuous content inspection is not justified merely by employer ownership of the system.
A documented communications policy
Explain permitted use, monitoring purposes and legal bases, scope, procedure, retention and possible consequences. Inform employees in a provable manner. A signed policy alone cannot make disproportionate or otherwise unlawful monitoring lawful.
5. Employee data policies and legal consequences
Compliance affects both data protection and employment disputes. Unlawfully obtained or inadequately disclosed information can raise questions about admissibility and the justification for dismissal. The outcome depends on the evidence and circumstances; it is not automatic.
Keep the privacy notice distinct from consent and make it accessible when data are collected.
Document lawful rules for attendance, cameras and communications monitoring.
Operate a procedure for access, correction and deletion requests, taking account of lawful retention duties.
Train managers and HR staff, set role-based access and confidentiality responsibilities.
Assess transfers to overseas group companies, service providers and other recipients under the international transfer rules addressed in the next part.
Official sources
- Law No. 6698, particularly Articles 4–6, 9, 10 and 12
- Board Decision 2026/921 on biometric attendance
- Authority guidance on workplace CCTV
- Constitutional Court: Fırat Gerçek, 21 September 2022
- Board Decision 2026/2035 on workplace communications
Related: Privacy notices and VERBIS.
Originally published: 30 September 2026. Legal references reviewed and updated: 30 October 2026. General information on Turkish law; not a substitute for advice on a specific matter.